VIAVI TeraVM Security Virtualized Application and Security Performance Validation Solution
Virtualized endpoint emulation platform for validating VPN, ZTNA, SASE, firewall and application security performance at scale.
- Cloud
- Amazon AWS, Google GCP, Microsoft Azure, Oracle OCI, Alibaba Cloud, OpenStack
- Hypervisors
- VMware ESXi, KVM (Ubuntu / RedHat)
- Containers
- Containers / Kubernetes – Google GKE, Amazon EKS
- Tunnelling overlays
- VxLAN, GRE; SR-IOV NIC passthrough
Overview
TeraVM Security is a fully virtualized application and security performance validation solution from VIAVI. It is used for functional and performance testing of network functions and service deployments, covering network and security devices such as secure VPN appliances, firewalls, enterprise call management devices, IMS Session Border Controllers and layer 4-7 application infrastructure. The datasheet describes it as an endpoint emulation platform providing per-endpoint emulation, control and reporting with automation, deployable on standard x86 servers and in cloud environments.
Secure access and VPN client emulation
TeraVM acts as many individual users on a network, including VPN-based users such as Cisco AnyConnect SSL and IPsec VPN clients running applications. Rather than simulating VPN traffic, it makes many individual valid connections to gateways such as Cisco FTD/ASA and sends and receives application flows, measuring VPN and application performance in real time. It supports clientless (SSL/TLS/DTLS) and client (IPsec IKEv1/v2) VPNs, a range of authentication, integrity and encryption algorithms, Single Sign On (SAML) and EAP-MD5 endpoint authentication, as well as client emulation for Palo Alto Prisma Access Agent, GlobalProtect and Cisco Secure Access.
Threat analysis
A cybersecurity threat database drawn from Common Vulnerability and Exposures (CVE) repositories lets users mix threat and malware traffic with genuine application traffic to assess security perimeter performance. Per-flow emulation of endpoints and applications supports validation of policy management solutions, including BYOD policies and blacklisted URL/DNS.
Post-Quantum Cryptography and SASE testing
TeraVM measures the performance overhead introduced by Post-Quantum Cryptography (PQC) in IKE/IPsec VPNs and TLS, including testing PQC and non-PQC clients in the same test and failover and fallback mechanisms. For Secure Access Service Edge (SASE) deployments it tests VPN link capacity, authenticated and unauthenticated web traffic, sustained connection counts, tunnel throughput, redundancy and latency-sensitive applications under load in the lab.
Virtual deployment
The same test tool is used for physical and virtual solutions. Test beds scale vertically and horizontally across locations, with test resources centrally managed and shared through a license server.
Key Features
- Elastic test bed that scales both vertically and horizontally
- Scales vertically from 1 Gigabit per second up to 1 Terabit per second
- Scales horizontally across test locations
- Central management and allocation of test resources via a license server
- License sharing for higher test bed utilization
- 100% virtual: same test tool for physical and virtual solutions
- Supports hypervisors ESXi and KVM
- Supports OpenStack, AWS, MS-Azure, Google Cloud, Oracle OCI and containerization
- Supports 1 GbE, 10 GbE, 40 and 100 GbE NICs
- REST, CLI, Perl, TCL, XML, Java API, Python and Jython automation
- Cisco LaasNG, Cisco pyATS and Qualisystems (CloudShell) integration
- L2-7 stateful traffic application emulation for voice, video and data
- Secure TCP/UDP protocols (SSL, TLS, DTLS, IPSec IKE)
- Client and clientless VPNs (Cisco AnyConnect SSL and IPsec)
- 802.1x EAP-MD5, EAP and PEAP with MS CHAPv2 authentication
- Mobile Secure Gateway validation (S1-U over IPSec)
- 40,000+ attacks (Spam, Viruses, DDoS, Malware), updated monthly
- DDoS floods: SYN, Reflective SYN, Reset, UDP, Ping, ARP
- Spoof MAC addressing
- Mixed good and bad application flows
- Site-to-site IKEv2 VPN testing with 100,000+ tunnels
- Post-Quantum Cryptography IKE/IPsec and TLS testing with ML-KEM
- QKD key management system test with ETSI 014 APIs
- Prisma Access Agent, GlobalProtect and Cisco Secure Access client emulation
- MASQUE ZTNA client emulation
- vRAN and vCORE emulation for 5G, 4G-LTE, 3G and 2G
- Error injection over 5G-N2 (AMF) and 4G-S1 (MME)
- WiFi ePDG offload (EoGRE)
- Adaptive engine to find maximum capacity of devices under test
- AI enablement: MCP server for test bed management and TestGen agent
Specifications
| Cloud | Amazon AWS, Google GCP, Microsoft Azure, Oracle OCI, Alibaba Cloud, OpenStack |
|---|---|
| Hypervisors | VMware ESXi, KVM (Ubuntu / RedHat) |
| Containers | Containers / Kubernetes – Google GKE, Amazon EKS |
| Tunnelling overlays | VxLAN, GRE; SR-IOV NIC passthrough |
| Multi-cloud | Distributed multi-cloud deployment support |
| I/O support |
1/10/25/40/100/200 Gbps
The web page lists 1 GbE, 10 GbE, 40 and 100 GbE NICs
|
|---|---|
| Vertical scaling | 1 Gigabit per second up to 1 Terabit per second |
| License management | System utilization reports and license management (Location, User, Testbed, usage stats, check-in timer) |
| Adaptive Engine | Automatically find maximum capacity of Devices Under Test |
| REST API | REST API for test management, real-time monitoring, and data export |
|---|---|
| Scripting interfaces | CLI, Perl, TCL, XML, Java API; Python, Jython |
| Integrations | QualiSystems (CloudShell), Luxoft SDL, OpenStack integration; Cisco LaasNG, Cisco pyATS |
| Site-to-Site VPN | Scalable Site-to-Site VPN – IPv4/IPv6 (100,000+ Tunnels/Subnets) |
|---|---|
| IKEv2 signature authentication | RFC 7427 IKEv2 with ECDSA; RFC 8420 IKEv2 with EdDSA |
| Prisma Access Agent VPN client emulation |
100,000+ Tunnels
Connecting to Prisma Access SASE cloud gateways
|
| Cisco AnyConnect VPN clients | Cisco AnyConnect TLS/DTLS/IKEv2 VPN Clients with 100,000+ scale, Dynamic IPv4 and IPv6 tunnel assignment |
| GlobalProtect authentication |
SAML 2.0, Certificate Only, and Certificate + Password auth; NGPA protocol
IPv4/IPv6 headends
|
| IKE/IPSec VPN with PQC | ML-KEMS FIPS-203, RFC9370, RFC9242 with 8 rounds of Key exchange |
|---|---|
| Post Quantum Preshared Key |
Post Quantum Preshared Key (PPK) (RFC8784)
ETSI 014 API for fetching keys
|
| TLS PQC | TLS PQC RFC10024 HTTPS with PQC ML-KEM FIPS-203 |
| PQC certificate testing | TLS PQC FIPS-204, FIPS-205 Certificate testing |
| QKD | QKD Key Management System Test with ETSI 014 APIs with IKEv2 Initiator and Responder emulation |
| 802.1x | 802.1x EAP-MD5, EAP and PEAP with MS-CHAPv2 |
|---|---|
| RADIUS client | RADIUS client EAP-TLS/EAP-FAST with configurable custom AVPs (10M+ Supplicants emulation) |
| Address assignment | Configurable MAC; DHCP; PPPoE (IPv4 and IPv6) |
| HTTP | HTTP/HTTPS, HTTP/2 (ALPN), HTTP/3 over QUIC; per-stream bitrate control and statistics |
|---|---|
| TLS Client Hello size |
up to 16KB
Configurable; spans multiple TCP segments
|
| TLS versions | TLS 1.3 and TLS 1.2 simultaneously on client and server; configurable TLS record size |
| DNS | DNS Client with UDP/TCP/TLS (DoT); DNS over HTTP (DoH); 1 million+ user-supplied DNS queries using random ports |
| VLAN Tagging | up to 8 concurrent tags |
| Congestion control | TCP CUBIC; L4S – TCP Prague |
| Cisco Netflow emulation |
v9 and v10(IPFIX)
Records/Exporter emulation at scale with user configurable and varying fields
|
| Multicast | IGMP v1/v2/v3 and MLD v1/v2 |
|---|---|
| Adaptive Bit Rate | HLS, HDS, MPEG-DASH, Smooth Streaming |
| Video codec | H.265 codec support |
| VoIP | SIP and RTP (secure and unsecure), SMS; auto-generated unique client scaling |
| G.711 SID support | RFC 3889 |
| Quality metrics | MOS, simultaneous, per end point |
| Threat database | 40,000+ attacks (Spam, Viruses, DDoS, Malware), updated monthly |
|---|---|
| DDoS flood | SYN, Reflective SYN, Reset, UDP, Ping, ARP |
| DDoS attacks | Teardrop; UDP Fragmentation; Configurable Rates, Start and Stop |
| Per flow measurements | per Session, per IP endpoint statistics |
|---|---|
| SLA monitoring | TWAMP – RFC 5357; PING – RFC 792 |
| Latency reporting | Latency/TCP RTT distribution view with bucket configuration; percentile reporting; CCDF plotting of TWAMP One Way Delay |
Specifications are taken from the manufacturer's documentation. See the datasheet for complete and current values.
Applications
- VPN appliance performance testing
- VPN client emulation
- SASE testing
- Zero Trust Network Access (ZTNA) validation
- Next Generation Firewall validation
- 5G Core firewall testing
- Cybersecurity threat analysis
- Post-Quantum Cryptography performance testing
- BYOD and access policy validation
- Session Border Controller testing
- Layer 4-7 application scalability testing
- NetSecOPEN test methodology
- NFV and cloud deployment validation
- Voice and video quality testing
Options & Accessories
| Option | Description |
|---|---|
| TVM3000 | Dell Server for Core Test — Support: HWSUP PPG15 (5G Core Security Test) |
| TVM3167 | 5G vRAN Emulator — Capacity: 1 User |
| TVM3160 | 5G vRAN Control Plane capacity — 100k UE, 1k gNB, 10k TPS |
| TVM3161 | 5G vRAN User Plane capacity — 1 License |
| TVM4104 | 5G Core Emulator — Capacity: 1 User |
| TVM4114 | 5G Core Emulator Control Plane capacity — 25 gNB, 1k UE, 1k TPS |
| TVM4115 | 5G Core Emulator User Plane capacity — 2.5 Gbps |
| TVM3152 | Application Traffic HTTP/FTP/OTT voice — 1 License |
| TVM4109 | IMS Server Emulation — 1 License |
| TVM3227 | Application Traffic UDP/TCP replay — 1 License |
| TVM3233 | Application Traffic HTTP streaming — 1 License |
| TVM3236 | Application Traffic SMTP — 1 License |
| TVM3157 | AWS Support — 1 License |
| TVM3168 | GCP Support — 1 License |
| TVM3159 | Azure Support — 1 License |
| 48000/319 | AMF Wraparound Test N1/2/8/11/12/14 — 100,000 TPS; support SA319 |
| 48000/317 | Error Insertion N1/N2 — 100,000 TPS; support SA317 |
| 48000/318 | AMF Mobility Test N26 — Requires 48000/319; 100,000 TPS; support SA318 |
| 48000/320 | SMF Wraparound Test N4/7/10/11 — 100,000 TPS; support SA320 |
| 48000/321 | UPF Wraparound Test N3/N4/N6 — 100 Gbps; support SA321 |
Documents & Resources
Related Products
Software-based RAN digital twin that simulates, develops and validates 4G, 5G, 6G and NTN network behavior and xApps/rApps without physical infrastructure.
Cloud-based platform that automates wireless test campaigns, cases and executions across VIAVI and third-party lab tools.
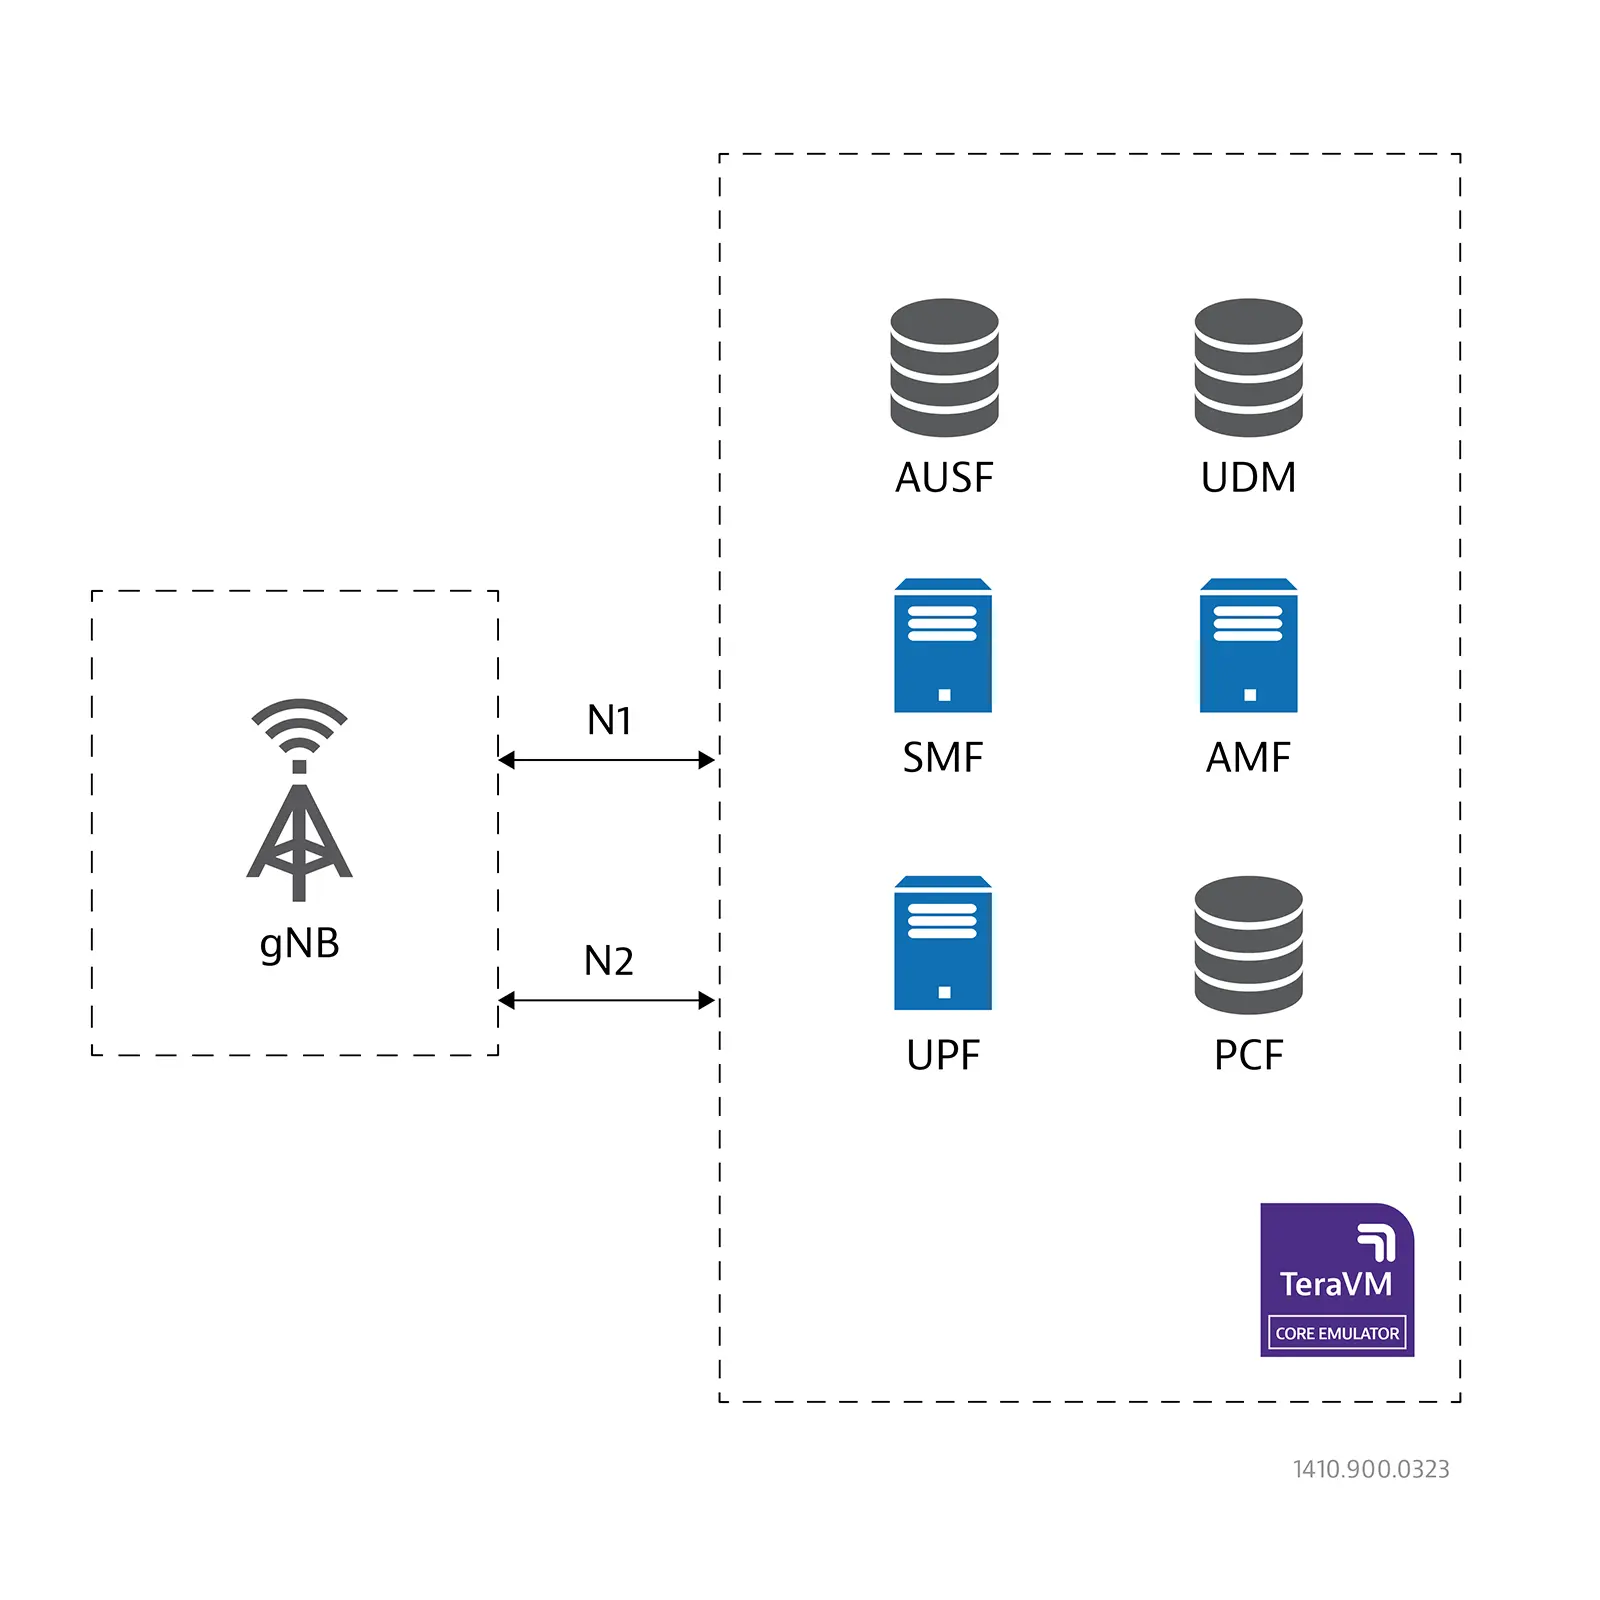
Virtualized 5G core network emulator that works with the TM500 test mobile for wrap-around testing of 5G gNBs in SA and NSA modes.
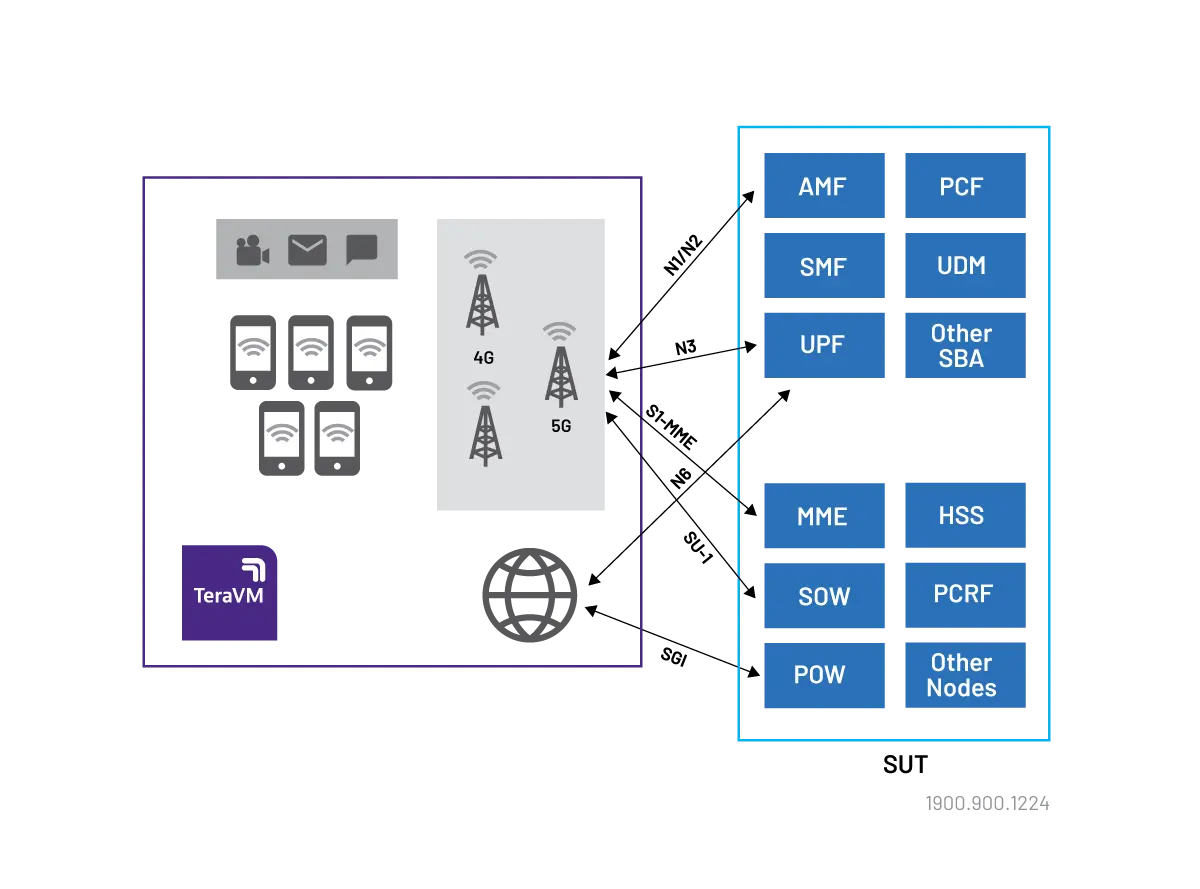
Virtualized test solution that emulates RAN, UEs and applications for full wraparound validation of 5G SA/NSA and 4G/3G/2G core networks.
Software-based O-CU subsystem tester that emulates O-DUs, UEs and core networks over F1, X2/Xn and S1/NG for O-RAN O-CU validation.
Software-only TeraVM test solution providing an elastic test bed for repeatable validation of virtualized, NFV and cloud networks.