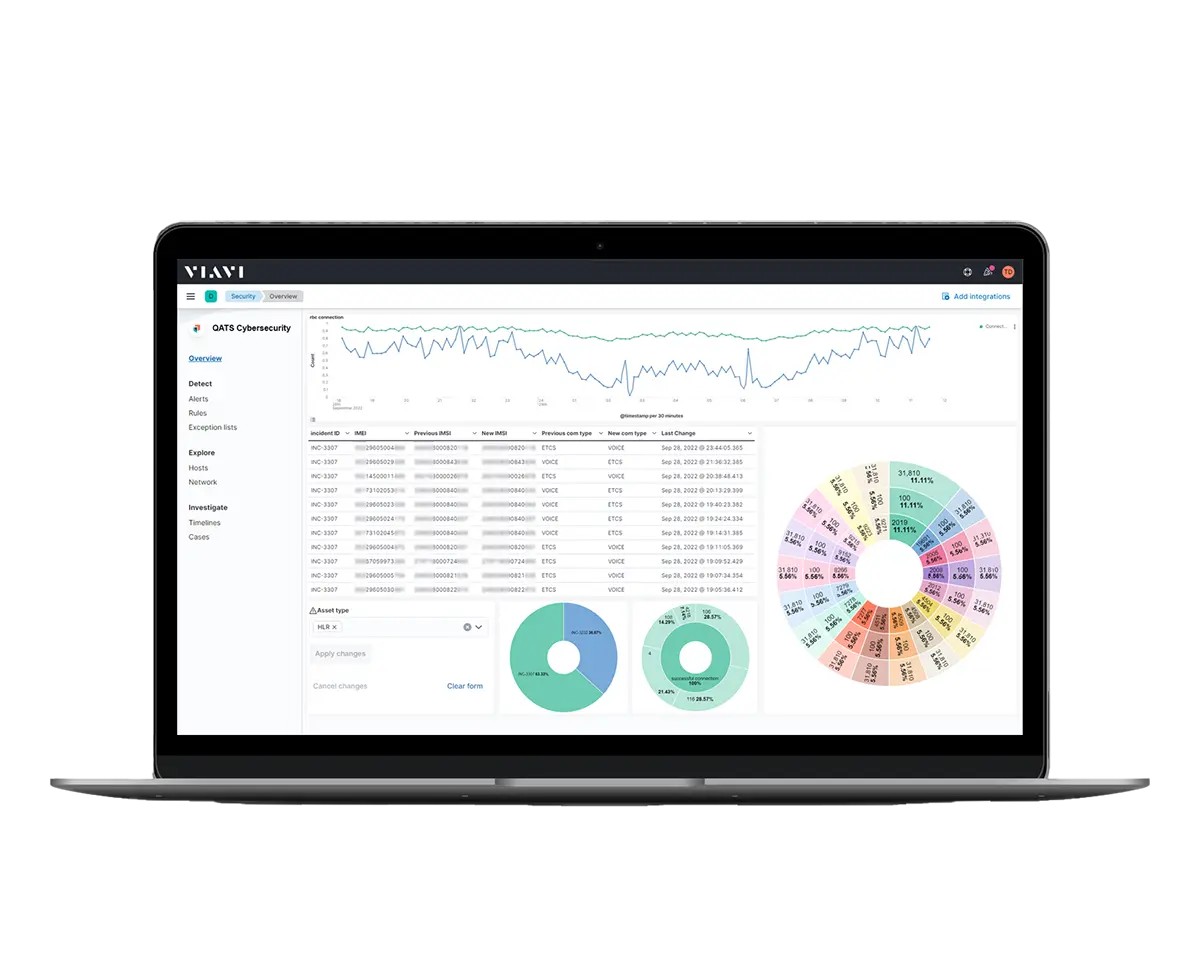
VIAVI EVOIA Cyber OT Cybersecurity Solution for Railway Telecommunication and Signalling Networks
Passive OT cybersecurity solution for MCx and railway telecom and signalling networks: 4G, 5G, FRMCS, GSM-R, GPRS and ETCS.
- Supported domains
- MCx, 4G, 5G, FRMCS, GSM-R, GPRS and ETCS
- Standards
- IEC 62443 and TS 50701
- Deployment
- Passive physical probes or agents; existing bandwidth or out-of-band
- Third-party integration
- Northbound Interface (NBI) export to SIEM and SOAR software (e.g. Splunk, QRadar, Elastic, Rapid7)
Overview
EVOIA Cyber is an operational technology (OT) cybersecurity solution for preventing and managing cyber-attacks on mission-critical (MCx) and railway telecommunication and signalling domains, including 4G, 5G, FRMCS, GSM-R, GPRS and ETCS.
IEC 62443 and TS 50701 requirements
The solution helps telecom, signalling and security operations personnel meet IEC 62443 and TS 50701 requirements. It monitors access from untrusted networks, audits records created by equipment and protects the integrity of information transmitted through the network. It also tracks unsuccessful login attempts, unauthorized wireless devices and tampering of information on any type of communication.
Passive implementation
EVOIA Cyber is non-intrusive and fully passive. It uses passive physical probes or agents to cover the railway network without interfering with it, and operates with minimal latency over the existing bandwidth or out-of-band.
Integration
EVOIA Cyber works with other solutions in the EVOIA portfolio, such as EVOIA Assure, and can reuse most of the same hardware and software components within the EVOIA architecture. It can also run as a standalone solution. A Northbound Interface (NBI) exports data to third-party SIEM and SOAR software, with support for providers such as Splunk, QRadar, Elastic and Rapid7.
Key Features
- Supports IEC 62443 and TS 50701 compliance requirements
- Recognizes information changes on all communication
- Covers everything from asset discovery to forensics with detailed analysis
- Designed for SOC, NOC, maintenance and security teams
- Runs as a standalone security solution or integrates with third-party SIEM or SOAR
- Non-intrusive and fully passive, using passive physical probes or agents
- Monitors access from untrusted networks
- Audits records created by equipment
- Tracks unsuccessful login attempts and unauthorized wireless devices
- Detects tampering of information on any type of communication
- Northbound Interface (NBI) for exporting data to third-party SIEM and SOAR software
- Reuses hardware and software components shared with the EVOIA portfolio, such as EVOIA Assure
Specifications
| Supported domains | MCx, 4G, 5G, FRMCS, GSM-R, GPRS and ETCS |
|---|---|
| Standards |
IEC 62443 and TS 50701
Requirements the solution helps meet
|
| Deployment | Passive physical probes or agents; existing bandwidth or out-of-band |
| Third-party integration | Northbound Interface (NBI) export to SIEM and SOAR software (e.g. Splunk, QRadar, Elastic, Rapid7) |
Applications
- Railway telecommunication networks
- Railway signalling networks
- Mission-critical (MCx) communications
- 4G and 5G networks
- FRMCS
- GSM-R
- GPRS
- ETCS
- Security operations centers (SOC)
- Network operations centers (NOC)